Upcoming · 45 min
Live now
Available on demand soon
On demand · 45 min
The 2026 NHI & AI Breach Report and the new PAM playbook
Most of 2026’s non-human identity and AI agent breaches started with a valid credential. Venice Field CTO Chris Maroun and Lalit Choda, founder of NHI Mgmt Group, unpack the breaches and the 2027 PAM playbook.
Learn more about using Venice. Book a demo
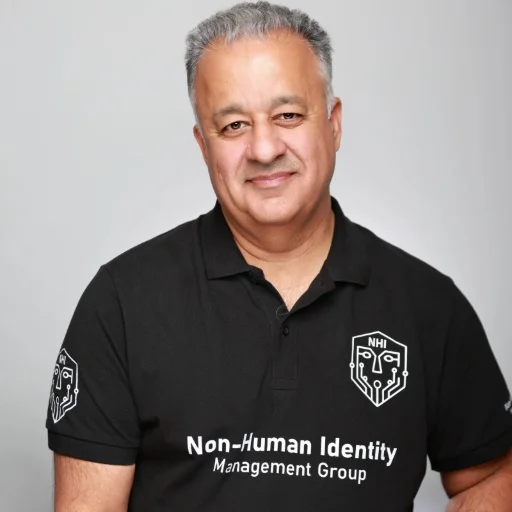
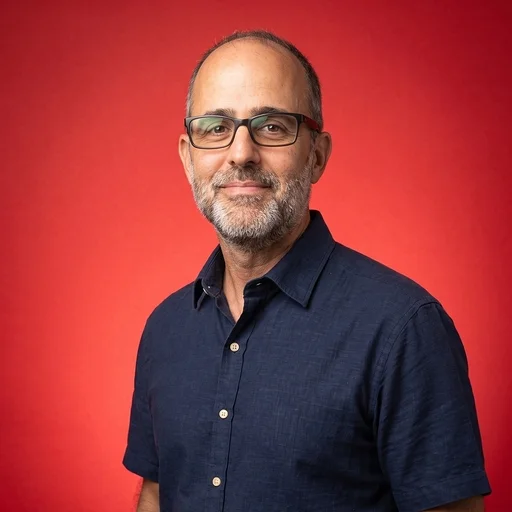
NHI Mgmt Group analyzed 234 real-world breaches involving non-human identities and AI agents, and 44% were credential-led. Most came down to a credential that never should have existed, or should have expired long ago.
Chris Maroun sits down with Lalit Choda (“Mr. NHI”) to unpack what 2026’s breaches reveal and where privileged access has to go in 2027. They’ll cover the patterns that keep repeating, why vaulting secrets isn’t enough, and how Venice removes standing credentials from scripts, pipelines, and AI agents with just-in-time access, so agents can act without ever holding a secret.
What you'll learnWhat you'll learnWhat's coveredWhat's covered
- Identify the entry routes behind this year’s NHI and AI agent breaches, and which ones to fix first
- Get a practical view of just-in-time access for workloads and agents, without hard-coded secrets
- Govern AI agents as identities, with an owner, least privilege, short-lived access, and a kill switch
- See how Venice brokers an agent’s request just in time, so the secret never reaches the agent
Presenters
Lalit Choda
Founder @ NHI Mgmt Group
Chris Maroun
Field CTO @ Venice
You'll also like
All webinarsPrivacy Preference Center
When you visit any website, it may store or retrieve information on your browser, mostly in the form of cookies. This information might be about you, your preferences or your device and is mostly used to make the site work as you expect it to. The information does not usually directly identify you, but it can give you a more personalized web experience. Because we respect your right to privacy, you can choose not to allow some types of cookies. Click on the different category headings to find out more and change our default settings. However, blocking some types of cookies may impact your experience of the site and the services we are able to offer. Learn more about cookie consent
Manage Consent Preferences
These cookies are essential for the website to function properly and cannot be disabled.
These cookies enable enhanced functionality and personalization, such as videos and live chat.
These cookies help us understand how visitors interact with our website by collecting anonymous information.
These cookies are used to track the effectiveness of our marketing campaigns.
We value your privacy
We use cookies to enhance your browsing experience, serve personalised ads or content, and analyse our traffic. By clicking "Accept All", you consent to our use of cookies.
